G/On is an integrated, scalable and secure remote access solution built on Zero-Trust principles — everything is on a need-to-know basis. It decreases your attack surface, increases visibility into user activity and reduces complexity. Plus, it delivers additional business benefits like BYOD, fast installation, scalability, affordability, permission access and a stable connection with no bandwidth issues.
G/ON Components
G/On Gateway
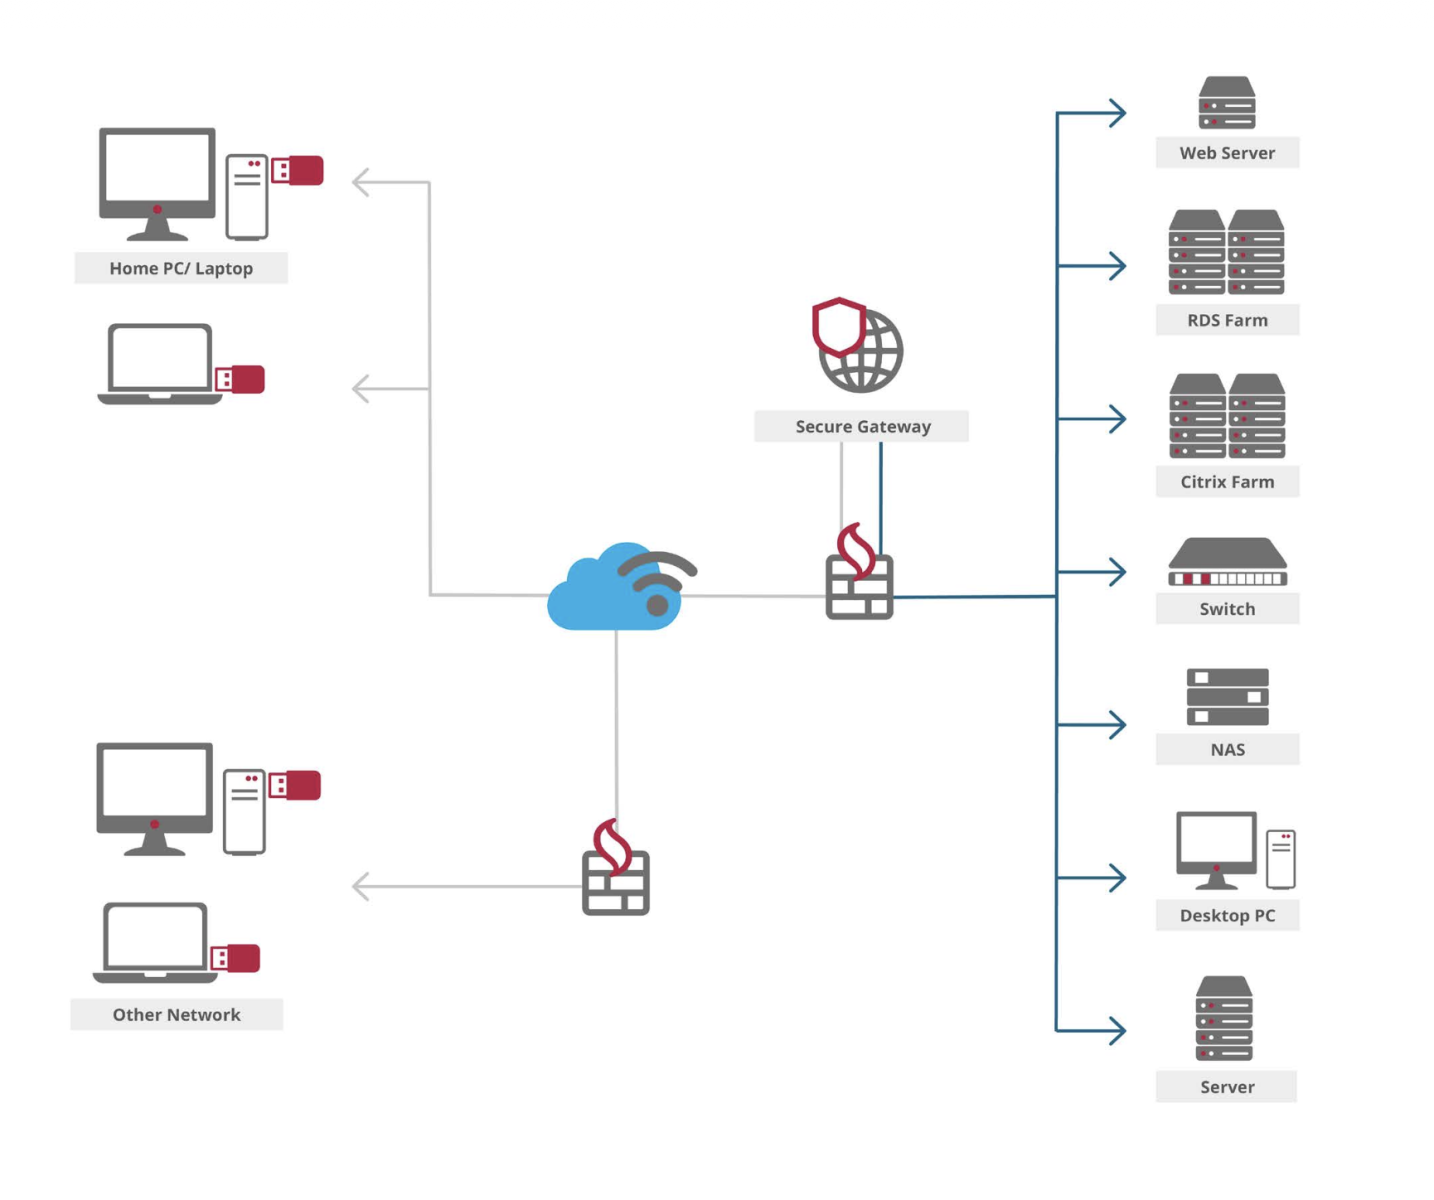
G/On Gateway hides the internal network and its resources from the Internet
-
Data in transit between the gateway and the remote client is encrypted using FIPS 140.2 certified AES 256-bit encryption.
-
Full application functionality at the client is created by using Proxy and DNS services from the internal network.
-
Built-in load-balancing and fail-over functionality, also works with third-party load-balancing products.
-
Additional gateways are easily created in seconds.
G/On Client
Connects applications on the client to resources inside the corporate network - without a VPN. After mutual two-factor authentication, the gateway server sends a dynamic menu to the client. This menu contains the specific applications available to the user, based on the device, authentication level, location, time and more.
Other features include:
-
The G/On client does not need to be installed.
-
No elevated rights are needed to run the application.
-
Users do not need to remember any URLs or other information to access applications.
-
Access rights are enforced in the gateway, preventing the user from starting not allowed applications or elevating access rights. Unavailable applications are not visible.
-
User menus can be adjusted in real time, even during active user sessions.
-
Automatic application launch and Single-Sign-On (SSO).
-
Ability to encapsulate all traffic in HTTP and traverse proxies without sacrificing security.
-
Includes application clients for RDP, Citrix, VNC, Browsers, File Access and much more.
G/On Management
Is the central web-based management console that controls one or more G/On Gateways and the behaviour of the clients:
-
Full control on users, applications, authentication levels and access authorization policies.
-
Granular application access based on individual permission rules or group membership.
-
Ability to control the behaviour of client applications– IT administrators can control the settings of client applications, e.g. to prevent copy/paste/download of files or allow the download of files in a dedicated secure environment.
-
Usage log – The SecureGateway logs all access attempts including details about which user, when and what resources are accessed by that user.
[Explore the G/ON solution brochure here]